Security Upgrade for AAS Addressing the Spring Framework Remote Command Execution Vulnerability
CNVD Vulnerability Platform Upgrade Announcement:
https://www.cnvd.org.cn/flaw/show/CNVD-2022-23932
How to upgrade AAS
1. The standard management console and the security management console of V9.0 use the Spring framework and must be upgraded using the attachment.
2. For the V9.0 series released after 2021, you can download the corresponding webtool.war and AAS-SecAdmin-V9.0.war from the Yunzhijia network disk, overwrite the existing files, and restart.
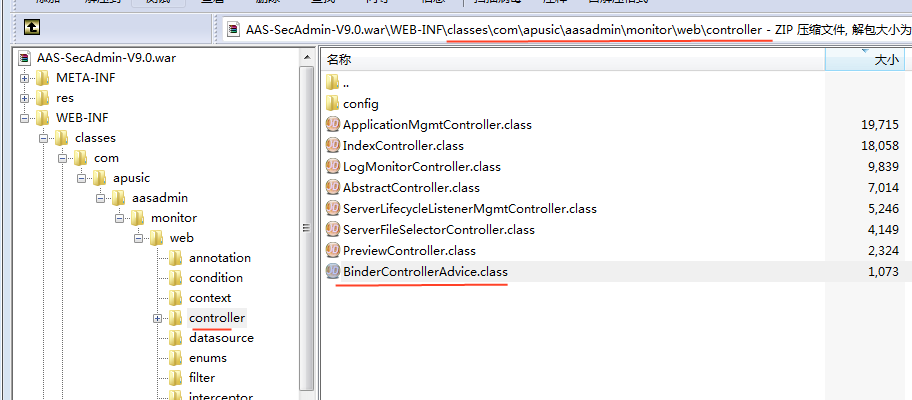
3. For older product versions, manual modification is recommended: open the console product package (webtool.war or AAS-SecAdmin-V9.0.war), place the attached BinderControllerAdvice.class into the corresponding subdirectory com\apusic\aasadmin\monitor\web\controller under the application's classes directory, as shown in the figure below, then save and restart AAS: