Remediation Instructions for the Security Vulnerability in Application Server V10.0
Recently, during use in a cloud platform project, an information disclosure vulnerability was detected in Application Server V10.0, internal ID AAS-5918. This document analyzes the issue and explains the solution, so that customers can update and fix the vulnerability in a timely manner, improve system security, and prevent security incidents.
Root Cause Analysis
Symptom: An application client can access unauthorized files by crafting a special path and obtain the file contents.
Cause: The application server's access path validation is not strict enough; requests with specially crafted paths bypass the check, causing file contents to be returned.
Affected scope: All Application Server V10.0 versions released before 2023-09-20 are affected.
Severity: High
Remediation
1. Patch download
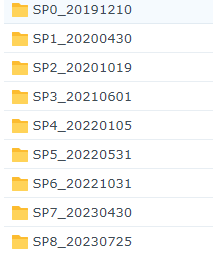
Each version of Application Server V10.0 requires a patch update. Currently released versions include the V10.0 base version and SP1 through SP8. Patch download address: http://file.apusic.com/sharing/7bdblw70g
The part after the underscore in the patch directory name indicates the release date of the corresponding version:
2. Update instructions
1) SP5 and later versions can be updated by uploading the patch through the patch management tool;
2) For SP4 and earlier versions, use aas-web-core.jar to directly replace the file with the same name under the ApusicAS/aas/modules/ directory, then delete the cache files under the ApusicAS/aas/domains/mydomain/osgi-cache directory, and restart the application server for the change to take effect;
3) If other patches have already been applied to the corresponding version or problems occur during the update, please contact the product department.
3. How to check the product version
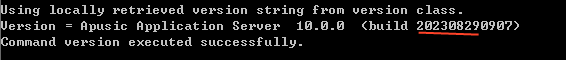
1. Use the asadmin command in the ApusicAS/aas/bin directory: enter asadmin version, and the following interface appears, with the date highlighted in red:
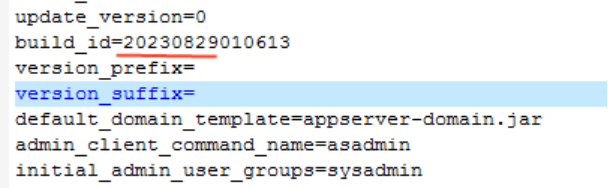
Configuration file: open ApusicAS/aas/config/aas-version.properties and check the build_id line, with the date highlighted in red: