Apusic Joins the Supply Chain Security Community as an Inaugural Member, Co-Building a Secure Software Supply Chain Ecosystem
Integration, Empowerment, Symbiosis
Apusic was recently named one of the inaugural members of the Supply Chain Security Community. On May 14, 2026, the community launched an open call for its first cohort of members. Following a rigorous selection process, 100 organizations were confirmed as inaugural members, with Apusic among them. This marks authoritative recognition of Apusic's professional capabilities and industry influence in software supply chain security.
What Is the Supply Chain Security Community?
The Supply Chain Security Community is a professional platform jointly established by the Fourth Research Institute of the Ministry of Industry and Information Technology (MIIT), the First Research Institute of the Ministry of Public Security, the State Information Center, the Institute of Information Engineering of the Chinese Academy of Sciences, the Zhongguancun Information Consumption Alliance, Zhejiang University, Beijing Institute of Technology, Huazhong University of Science and Technology, and Tianjin University. Created to thoroughly implement national decisions and plans on industrial and supply chain security, it aims to promote high-quality software development and a high level of security. The community pools high-quality resources across industry, academia, research, and application, and is committed to building a collaborative platform for discussion and exchange, joint research, coordinated action, and shared governance — systematically strengthening security governance across the full software lifecycle of design, development, testing, procurement, delivery, and operations.
The selection of the first 100 members was rigorous, spanning a wide range of market players and research institutes deeply engaged in software operations, core technology R&D, cybersecurity governance, and third-party testing services. Making the inaugural list signals that an organization possesses solid professional capabilities, a strong industry reputation, and a sustained commitment to software supply chain security.
Why Does Software Supply Chain Security Matter?
Software supply chain security refers to a comprehensive set of security practices for identifying, assessing, defending against, monitoring, and governing risks across every link involved in a software product's full lifecycle — "design, development, build, release, procurement, deployment, operation, and retirement" — including "developers, suppliers, open-source components, build toolchains, distribution channels, dependencies, and operating environments." Against the backdrop of accelerating digital transformation, software has become critical infrastructure underpinning economic and social activity, and the security and stability of the software supply chain directly affect business continuity, the safety of data assets, and the overall resilience of industrial chains.
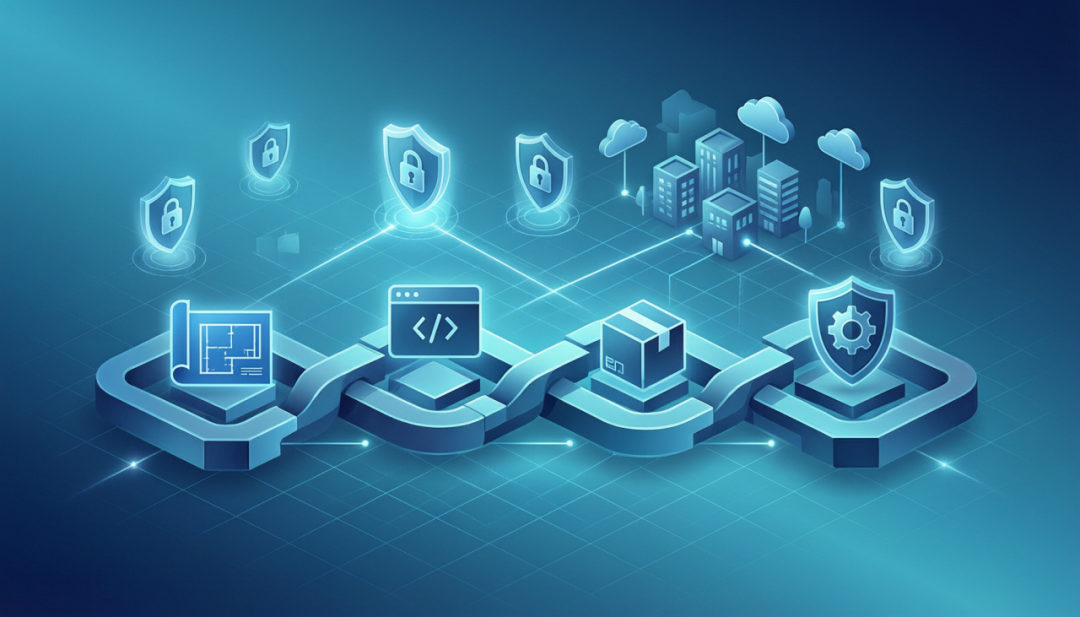
Once a vulnerability or risk emerges at any point in the software supply chain, it can propagate rapidly along the chain and trigger systemic security incidents. Strengthening software supply chain security governance is therefore both a practical necessity for enterprises seeking to cut costs, boost efficiency, and operate steadily, and an important pillar for safeguarding national industrial and supply chain security and promoting the healthy development of the digital economy.
What Does Inaugural Membership Mean for Apusic?
As a representative enterprise in China's domestic foundational software sector, Apusic has continuously invested in domestic middleware R&D, cybersecurity governance, and core technology innovation. Being selected in the first cohort reflects the industry's high recognition of our technical strength and compliance capabilities. Joining the community is not only an honor — it also means Apusic will take on responsibility for co-building software supply chain security standards, conducting joint technology research, and co-governing the ecosystem. Relying on the community platform, Apusic will deepen collaboration with all parties across industry, academia, research, and application, continuously improve full-lifecycle software security governance, and deliver more secure and trustworthy products and services to customers.
Conclusion
Supply chain security has no finish line — only a continuous journey forward. Apusic will take its inaugural membership as a new starting point, actively participate in building the Supply Chain Security Community, and work with all members to jointly fortify the software supply chain security line of defense and safeguard the high-quality development of the digital economy.
Latest News
Driving Innovation and Development in China's Foundational Software Industry
Driving innovation and development in China's foundational software industry
High-Quality Development: Interim Results Review